If your company works with the Department of Defense — or wants to — CMMC can determine eligibility for solicitations and contracts that require a specific CMMC status. Right now the program sits in an unusual position: Phase 2 and later implementation milestones are suspended, while Phase 1 self-assessment requirements and underlying FAR/DFARS safeguarding obligations remain in effect.
That combination is where contractors get into trouble. The headline says "suspended." The legal exposure says otherwise, and the Justice Department has spent 2026 proving it.
This guide covers what CMMC 2.0 is, which level applies to you, what the suspension actually changed, and what it did not.
Where CMMC 2.0 Stands Right Now
On July 13, 2026, DoD announced the immediate suspension of CMMC Phase 2 requirements — the third-party C3PAO assessment milestone that had been scheduled to take effect on November 10, 2026 — along with later implementation milestones. The CMMC Reform Task Force was directed to deliver a final report to the Department CIO within 60 days. No public replacement Phase 2 schedule has been announced; Phase 1 self-assessment requirements remain in effect, and Phase 2 remains suspended. During the suspension, the Department is enforcing NIST SP 800-171 Rev. 2 through self-assessments and select government-led assessments. The underlying Level 2 (C3PAO) provisions remain in 32 CFR Part 170; their Phase 2 implementation has been suspended, not eliminated.
Last reviewed: September 21, 2026
The stated rationale was cost and administrative burden for contractors. A public Request for Information sought industry input on cost drivers and program burdens, with responses due August 14, 2026.
Here is what did not change:
- Phase 1 remains firmly in place. It took effect November 10, 2025 and currently permits Level 1 annual self-assessments and Level 2 (Self) assessments every three years, with the applicable affirmations entered in SPRS.
- DFARS 252.204-7012 remains in force, including the obligation to safeguard covered defense information and report incidents within 72 hours.
- NIST SP 800-171 Rev 2 continues to be enforced — through self-assessments and select government-led assessments.
- Prime contractor flow-down obligations remain contractual.
The distinction that matters: the pause affects when and how implementation gets independently verified. It does not suspend the duty to implement the requirements.
The Suspension Does Not Reduce Your Legal Exposure
This is the part most coverage of the suspension leaves out, and it is the part with financial consequences.
The Department of Justice's Civil Cyber-Fraud Initiative uses the False Claims Act to pursue contractors whose cybersecurity representations allegedly do not match their contractual obligations or actual practices. That enforcement did not pause with CMMC Phase 2.
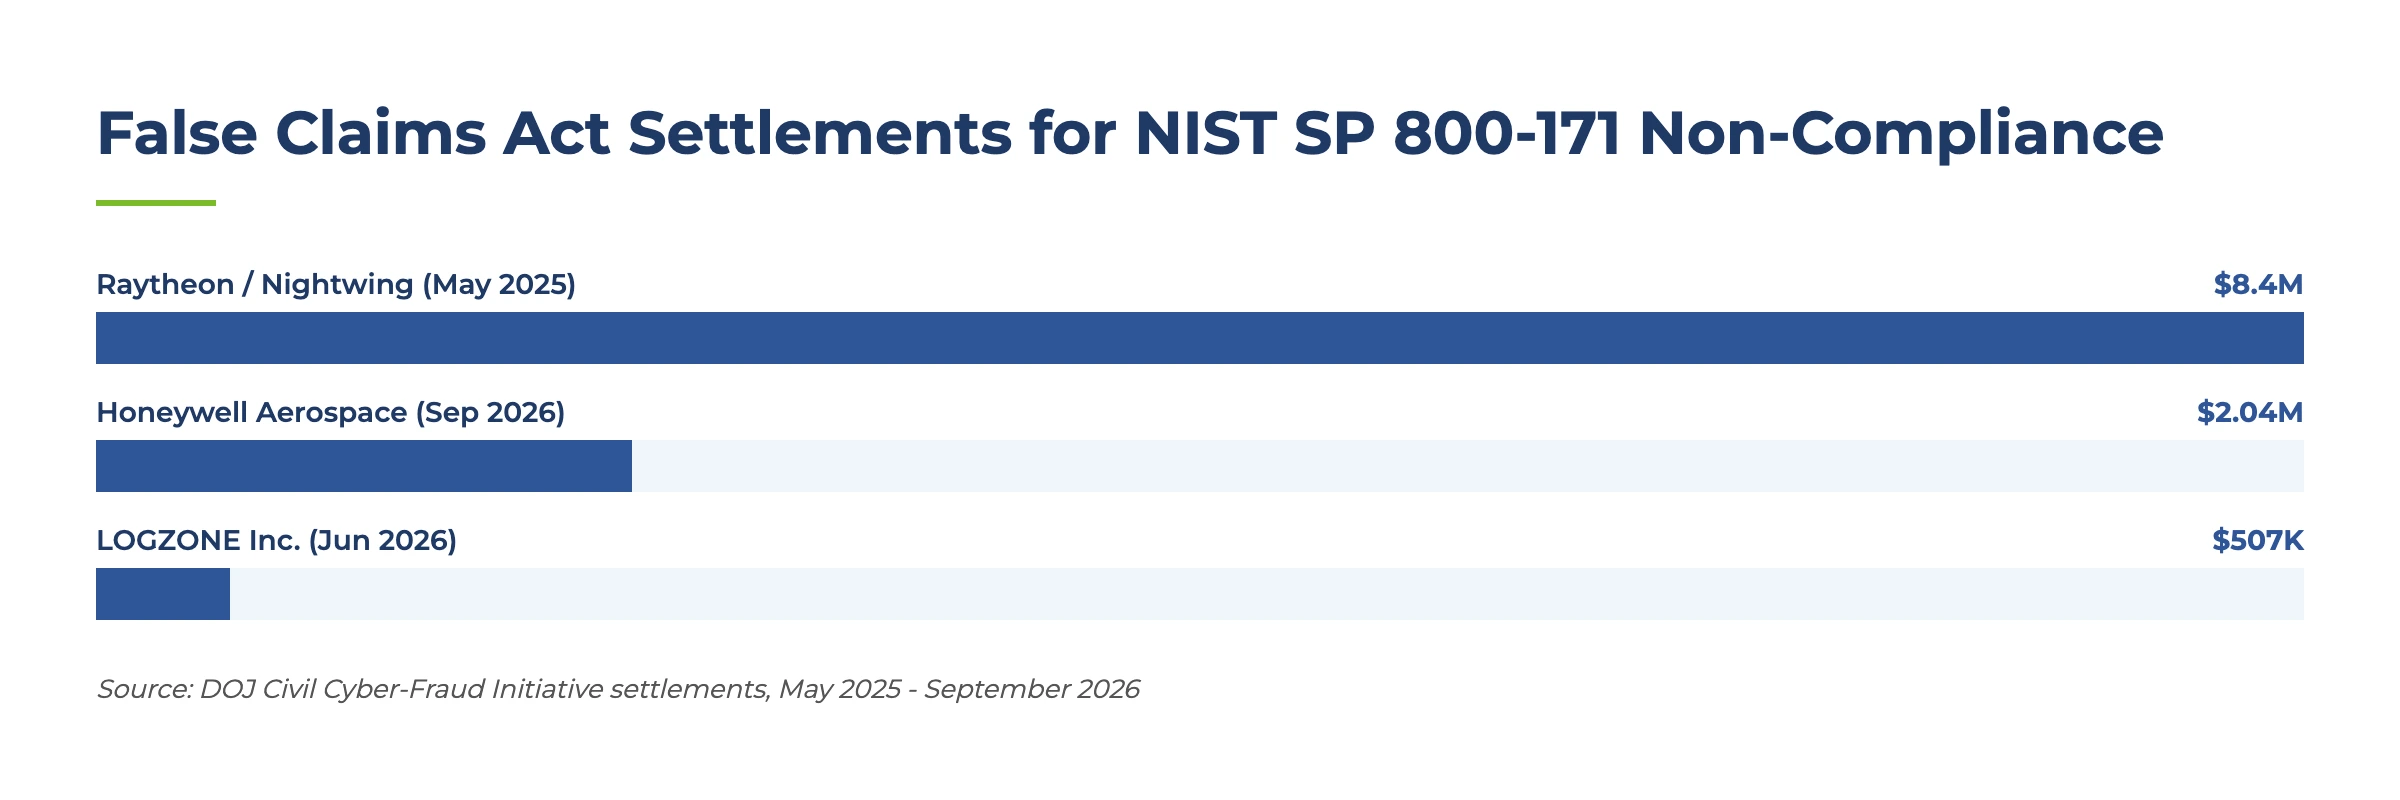
The LOGZONE case is the one every contractor should read twice. The Alabama defense contractor submitted a self-assessment score of 110 — a perfect score — in October 2021. When the government conducted its own assessment in February 2024, the score came back at -170, near the bottom of the scoring range. LOGZONE settled for $507,144 in June 2026, including $253,572 in restitution, over claims submitted to the Navy between May 2021 and March 2025.
Honeywell Aerospace settled for $2,042,518 on September 1, 2026 — weeks after the suspension — over allegations it failed to comply with NIST SP 800-171 controls on one of its networks between April 2020 and December 2023. The whistleblower received $375,823.
Raytheon and Nightwing agreed to pay $8.4 million in a settlement announced May 1, 2025, resolving allegations involving 29 DoD contracts and subcontracts.
DOJ's recent cases demonstrate that cybersecurity representations, including assessment-related representations, can later be scrutinized under the False Claims Act.
Read that against the current moment. During Phase 1, self-assessment is the operative CMMC mechanism. An inaccurate SPRS score is therefore not merely an administrative issue; if a materially false representation is made knowingly, it can create contractual and False Claims Act exposure.
What CMMC 2.0 Actually Is
CMMC stands for Cybersecurity Maturity Model Certification. It is the Department of Defense framework for verifying implementation of cybersecurity requirements protecting Federal Contract Information (FCI) and Controlled Unclassified Information (CUI) across the Defense Industrial Base, governed by 32 CFR Part 170.
Under CMMC, contractors and subcontractors must achieve the CMMC status specified in an applicable solicitation or contract. During the current Phase 1 pause, the program may require only Level 1 and Level 2 self-assessment statuses. The framework largely verifies implementation of existing FAR/DFARS safeguarding requirements rather than creating a separate replacement security standard.
How CMMC 2.0 Differs from CMMC 1.0
In November 2021, amid significant confusion about the maturity levels and who they applied to, DoD announced changes to the original model — now called CMMC 1.0. The headline change was structural: five maturity levels became three.
Under CMMC 1.0, Levels 2 and 4 functioned as transitional stages toward the next level rather than certification targets in their own right. CMMC 2.0 removed them and consolidated the model into the three levels in use today, changing the assessment and certification processes alongside the level structure.
The Three Levels of CMMC 2.0
Your required level is determined by the type of information you handle and the requirements written into your contract — not by company size or preference.
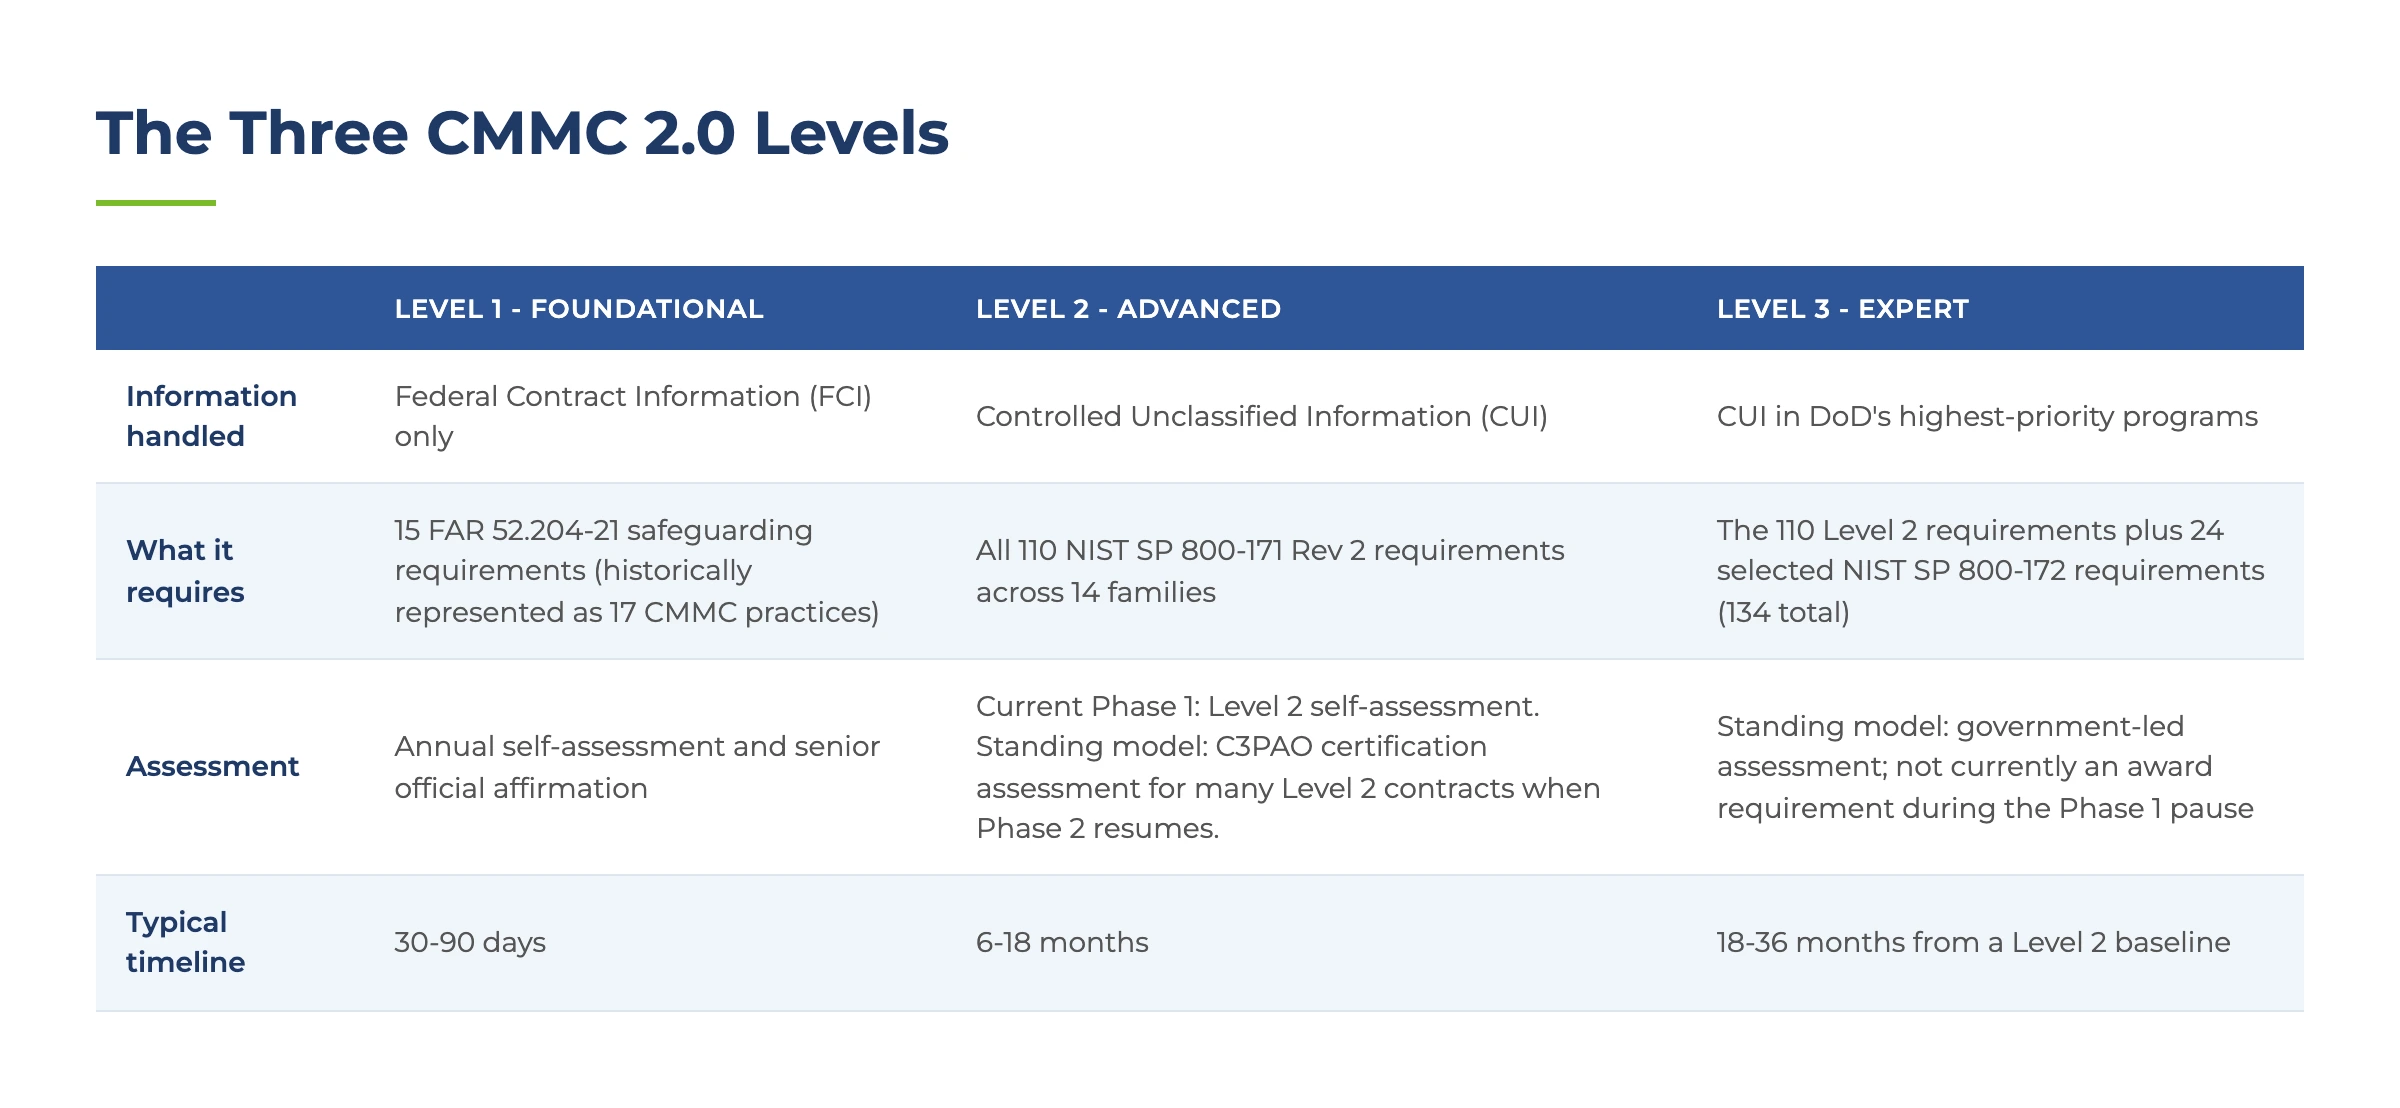
Many contractors handling CUI will fall within Level 2 when the applicable solicitation or contract requires that status. Technical drawings, engineering data, or government-specified information should not be assumed to be CUI solely by description; scope depends on the information designation and contract requirements.
For deeper detail on each tier, see our guides to CMMC Level 1 requirements and CMMC Level 2 requirements.
Who Needs CMMC Certification?
The obligation reaches further down the supply chain than many companies expect. It applies to:
- Subcontractors and sub-tier suppliers holding DoD contracts
- Any company handling CUI under DFARS clauses
- Suppliers throughout the Defense Industrial Base, including those without a dedicated cybersecurity team
That last group is where pressure concentrates. Prime contractor compliance officers may use approved-vendor lists and cybersecurity questionnaires to manage supply-chain risk. A subcontractor that cannot demonstrate required cybersecurity posture may lose an award or future opportunities.
The Rollout Timeline and Where It Stopped
CMMC 2.0 was designed to phase in over several years, each phase widening the set of contracts and assessment types in scope.

Phase 1 obligations continue while the program remains paused in Phase 1. The suspension applies to Phase 2 and later implementation milestones pending further Department guidance.
What CMMC 2.0 Actually Requires
For Level 2, readiness comes down to six things:
NIST SP 800-171 alignment. Final Level 2 status requires implementation of all 110 NIST SP 800-171 Rev 2 security requirements across 14 families. Limited POA&M use may support Conditional Level 2 status only for eligible requirements and must be closed out within 180 days.
A System Security Plan (SSP). A complete, current document showing how each requirement is implemented across your environment. This is the first artifact an assessor reviews, and a generic or outdated one is among the most common reasons assessments stall.
A Plan of Action and Milestones (POA&M). CMMC permits only limited POA&M use at Level 2: the assessment must meet the threshold for Conditional status, only eligible requirements may be deferred, and closeout is required within 180 days.
Access control and incident response. Documented controls for CUI access, audit logging, multi-factor authentication, and incident reporting.
Third-party assessment. Under the standing CMMC model, many Level 2 certification assessments are performed by C3PAOs authorized through The Cyber AB. The Phase 2 milestone that would expand third-party assessment requirements is currently suspended.
Annual affirmation. A senior company official affirms your security posture to the SPRS database each year.
Meeting the standard is not the whole job. You have to be able to prove it. Assessors evaluate documented evidence, not intent, and the gap between doing the work and evidencing it is where most small and mid-size contractors get caught. As LOGZONE demonstrates, that gap is now measured in dollars.
How CMMC 2.0 Relates to NIST 800-171 and DFARS
If your contracts already include DFARS 252.204-7012, you are already subject to NIST SP 800-171. That clause requires contractors handling CUI to implement those security requirements and to report cyber incidents to DoD within 72 hours.
CMMC 2.0 builds on that foundation by adding a contract-linked assessment and affirmation framework around the same 110 Level 2 requirements. Depending on the CMMC status and implementation phase, verification may be a self-assessment, third-party assessment, or government assessment. The underlying Level 2 security requirements remain NIST SP 800-171 Rev 2.
One consequence catches contractors repeatedly: DFARS 252.204-7012 imposes specific requirements when an external cloud service provider stores, processes, or transmits covered defense information. The provider must meet security requirements equivalent to the FedRAMP Moderate baseline and specified incident-response obligations. Microsoft 365 GCC and GCC High support different government scenarios; GCC High is designed for DoD IL4 and ITAR-sensitive workloads. CMMC itself does not impose a single universal “data sovereignty” rule requiring GCC High for every CUI environment.
How to Prepare
First-time NIST SP 800-171 gap assessments often surface substantial implementation gaps. The useful question is not the raw gap count but how the findings are sequenced by scope, dependency, risk, and implementation effort.
A structured path to Level 2 readiness looks like this:
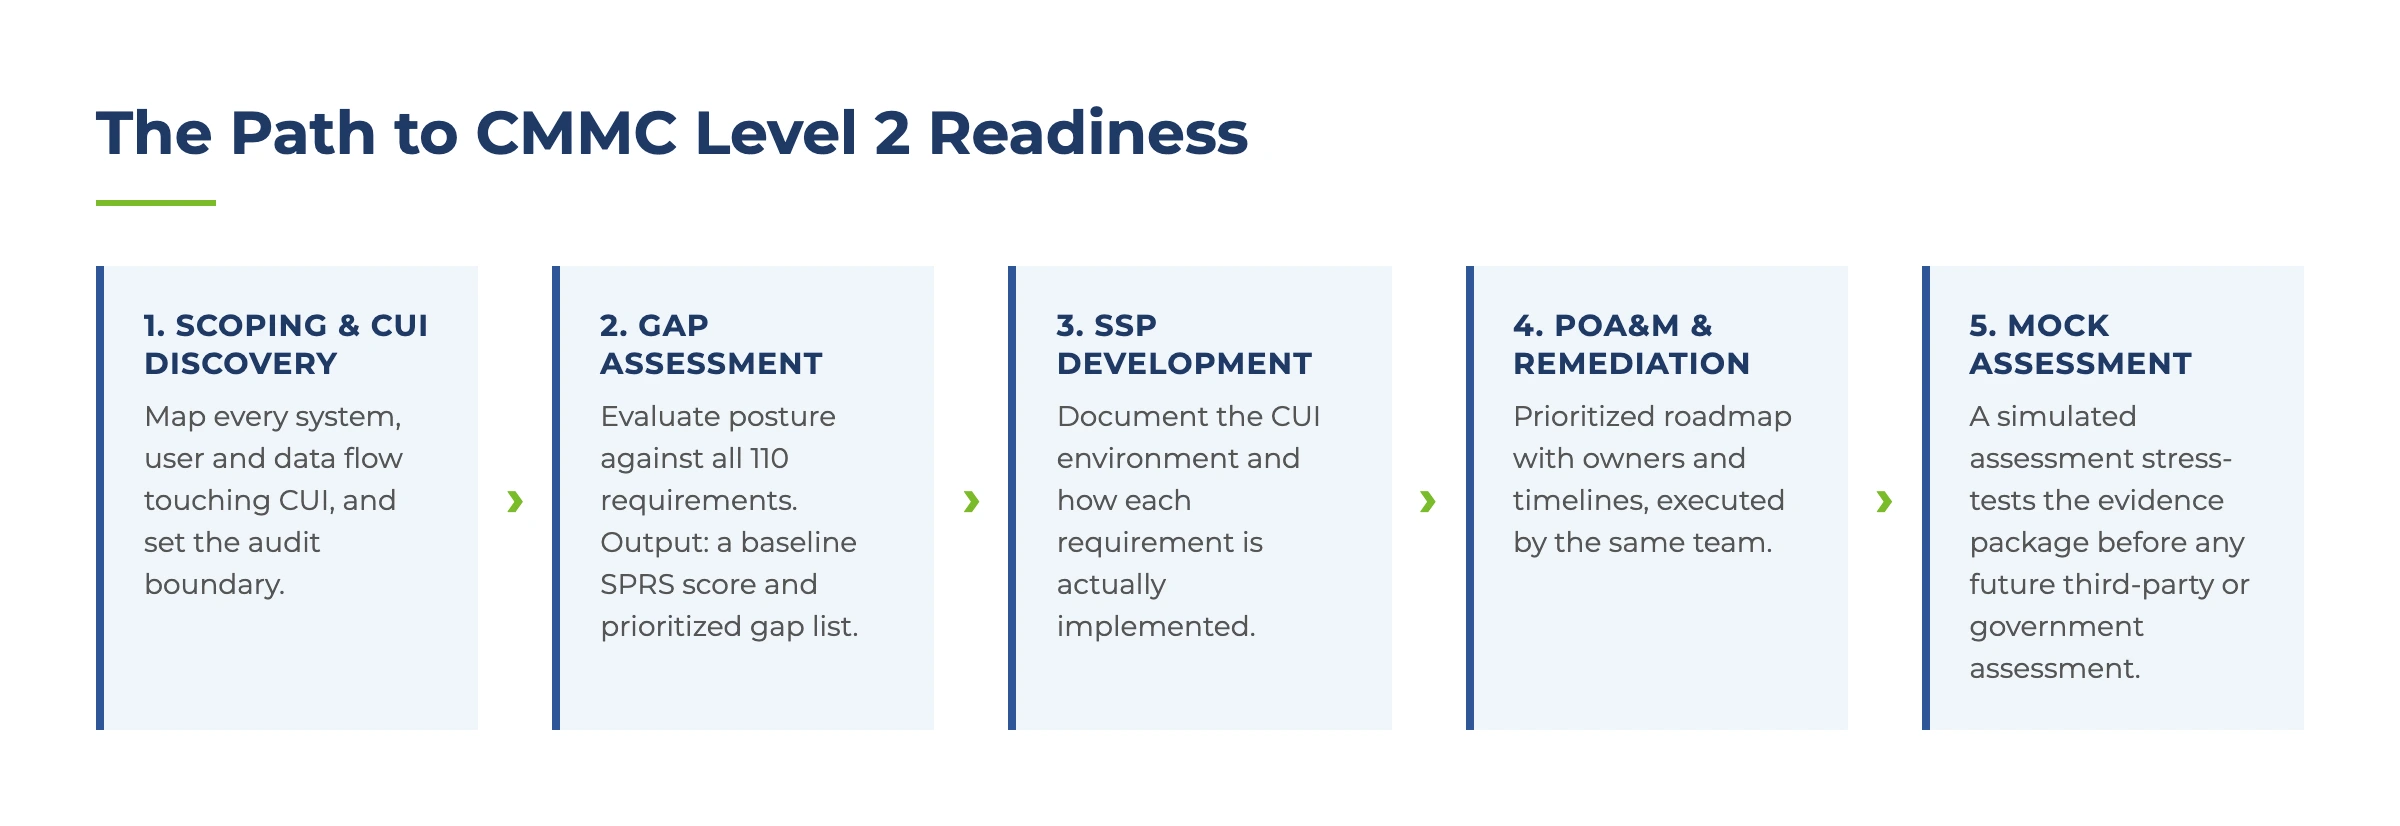
Scope is one of the most consequential decisions in the effort, because it determines what gets assessed, remediated, and maintained. Concentrating CUI into a properly designed controlled enclave can shrink the assessment boundary. GCC High may be appropriate where contract, CUI category, ITAR, or DoD impact-level requirements call for it; the platform choice should follow the scoped requirement.
The economics are worth understanding before you start. Third-party assessment cost varies materially with scope, environment complexity, assessor, and readiness. That variability makes accurate scoping and evidence preparation important before engaging a C3PAO.
Frequently Asked Questions
What is the current status of CMMC 2.0 enforcement?
On July 13, 2026, the Department suspended CMMC Phase 2 — the third-party assessment milestone scheduled for November 10, 2026 — along with pending and future implementation milestones. The Reform Task Force was directed to deliver a final report to the Department CIO within 60 days. No public replacement Phase 2 schedule has been announced; Phase 1 self-assessment requirements remain in effect. DFARS 252.204-7012 and applicable NIST SP 800-171 Rev 2, SPRS, affirmation, and flow-down obligations remain in force.
Does the suspension reduce my legal risk?
No. DOJ's Civil Cyber-Fraud Initiative continues to pursue False Claims Act cases over cybersecurity misrepresentation, with settlements in 2026 including Honeywell Aerospace at $2,042,518 and LOGZONE at $507,144. Because self-assessment is the operative mechanism during the suspension, an inaccurate SPRS score carries more exposure right now, not less.
What is the difference between CMMC Level 1 and Level 2?
Level 1 addresses FCI and currently requires annual self-assessment and affirmation against the 15 FAR 52.204-21 safeguarding requirements (historically represented as 17 CMMC practices). Level 2 addresses CUI and uses all 110 NIST SP 800-171 Rev 2 requirements. During Phase 1, Level 2 (Self) is the operative CMMC assessment path; the standing model includes C3PAO certification assessments when later implementation phases resume.
Do I need a C3PAO to become certified?
Not as a current Phase 1 award requirement. The Department states that CMMC is paused in Phase 1 and may presently require only Level 1 and Level 2 self-assessments. Under the standing model, many Level 2 certification assessments would be conducted by a C3PAO authorized through The Cyber AB when Phase 2 resumes. Abel Solutions is not a C3PAO; we prepare organizations for assessment while keeping the certification function independent.
How long does CMMC Level 2 readiness take?
Most SMBs require 6 to 18 months from initial gap assessment to C3PAO readiness. The timeline depends on your starting gap count, your team's bandwidth, and whether gaps are technical (often faster) or organizational and policy-based (often slower). Organizations already invested in Microsoft 365 security tooling and GCC High environments tend to start further along.
What is a System Security Plan and do I need one?
An SSP is a formal document describing how your organization implements each of the 110 NIST SP 800-171 requirements — your IT environment, the CUI you handle, your access control policies, and the technical and administrative measures in place. Level 2 requires a complete, current SSP, and assessors evaluate it thoroughly. If you do not have one, it is usually the first major documentation effort to tackle.
Is CMMC a one-time certification?
No. Level 2 is a three-year obligation. Every year a senior official must affirm your security posture to SPRS, your SSP must stay current as your environment changes, and a triennial reassessment follows. Assessors look for evidence of continuous implementation, not a program assembled for an assessment and set aside.
Use the Window While It's Open
The suspension did not change applicable NIST SP 800-171 obligations, SPRS and affirmation requirements, or contractual flow-down duties. What it opened is time to assess your real posture, close the gaps that matter, and make your self-assessment defensible while Phase 2 remains suspended and before independent verification requirements expand again.
Abel Solutions provides structured CMMC consulting for defense contractors of all sizes. As part of SGS/ATS, a global Testing, Inspection, and Certification organization, we will be here for your next assessment cycle and the one after that.